Access boundaries
Agents use scoped accounts and only the data and actions a workflow needs.
Identity and accessSecurity & governance
Agents act on business systems, so security is designed into every workflow: who can access what, which actions need approval and what is recorded.
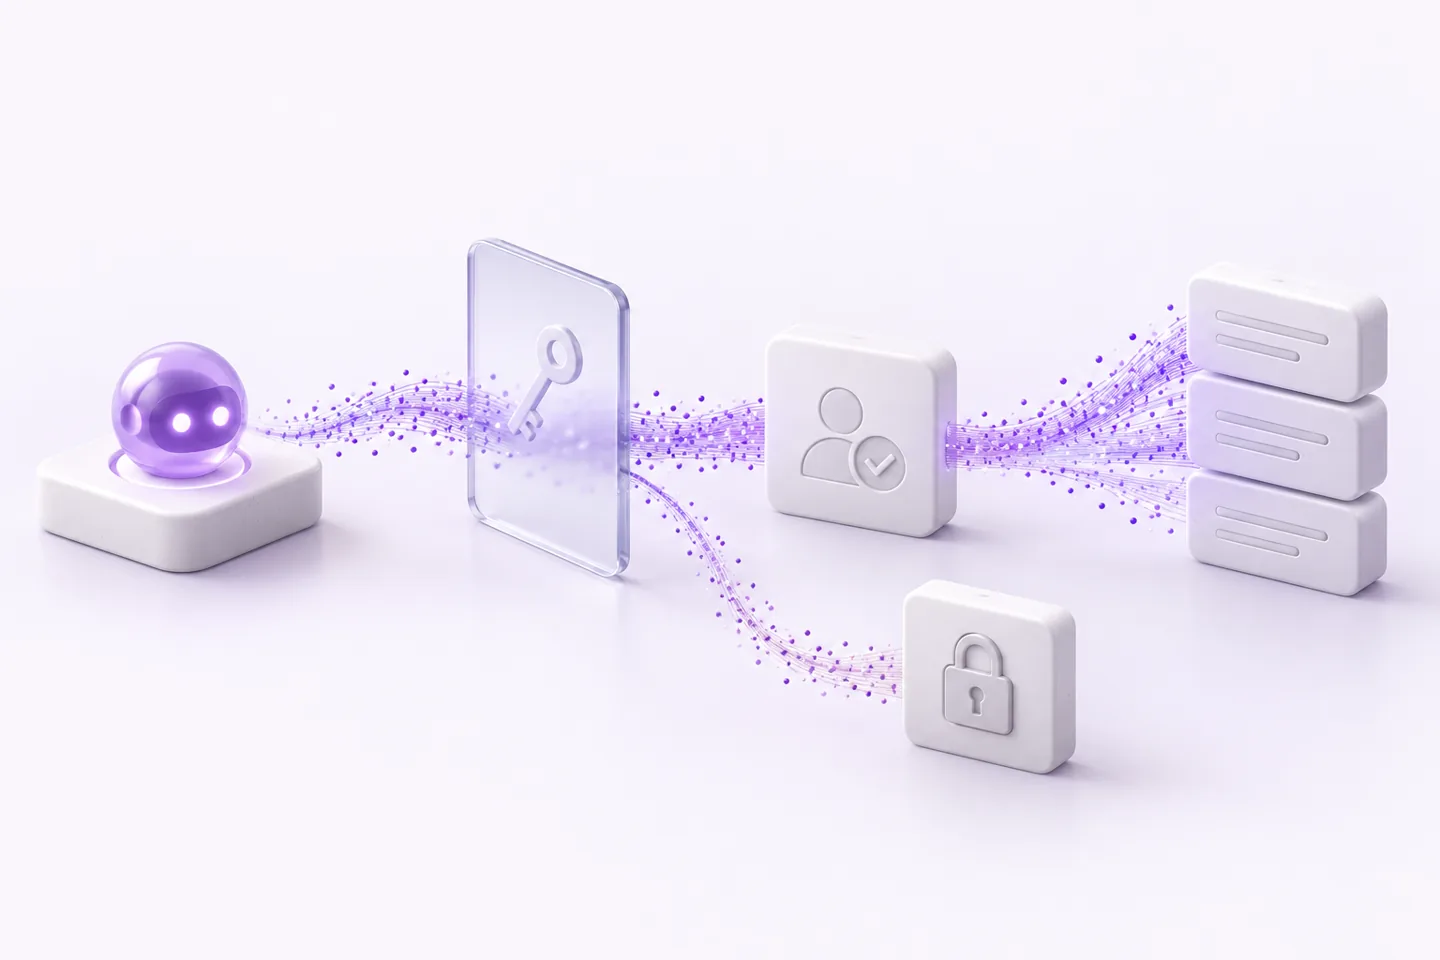
Controls are agreed per implementation and documented before launch.
Agents use scoped accounts and only the data and actions a workflow needs.
Identity and accessActions, decisions and approvals are logged for review.
Auditability and logsPolicy checks, approval thresholds and stop conditions keep autonomy within limits.
GuardrailsFrom scoping to operation.
Identify data, systems and risks for the workflow.
Agree access, approvals, retention and logging.
Check actions and failure cases before launch.
Monitor, review exceptions and manage changes.
We welcome your security questionnaire.
Ask us about the current status for your project. We do not claim certifications on this page; we answer security questionnaires and document the controls agreed for each implementation.
The model, speech and hosting providers are chosen and disclosed per project, so you can review them before launch.
We choose the model and provider for each task during scoping, based on the language, accuracy, latency and data-handling requirements. The workflow is not tied to one provider, so a step can be changed later if the agreed requirements change.
Discovery call
Bring us a process, a recurring enquiry or a pile of documents. We will explore where agents fit and what a useful implementation needs.
Book a discovery call