Policy checks
Validate inputs and proposed actions against agreed rules before anything is written.
Security & governance
Guardrails keep agents within agreed limits: policy checks before actions, approval thresholds for sensitive steps and stop conditions when something is uncertain.
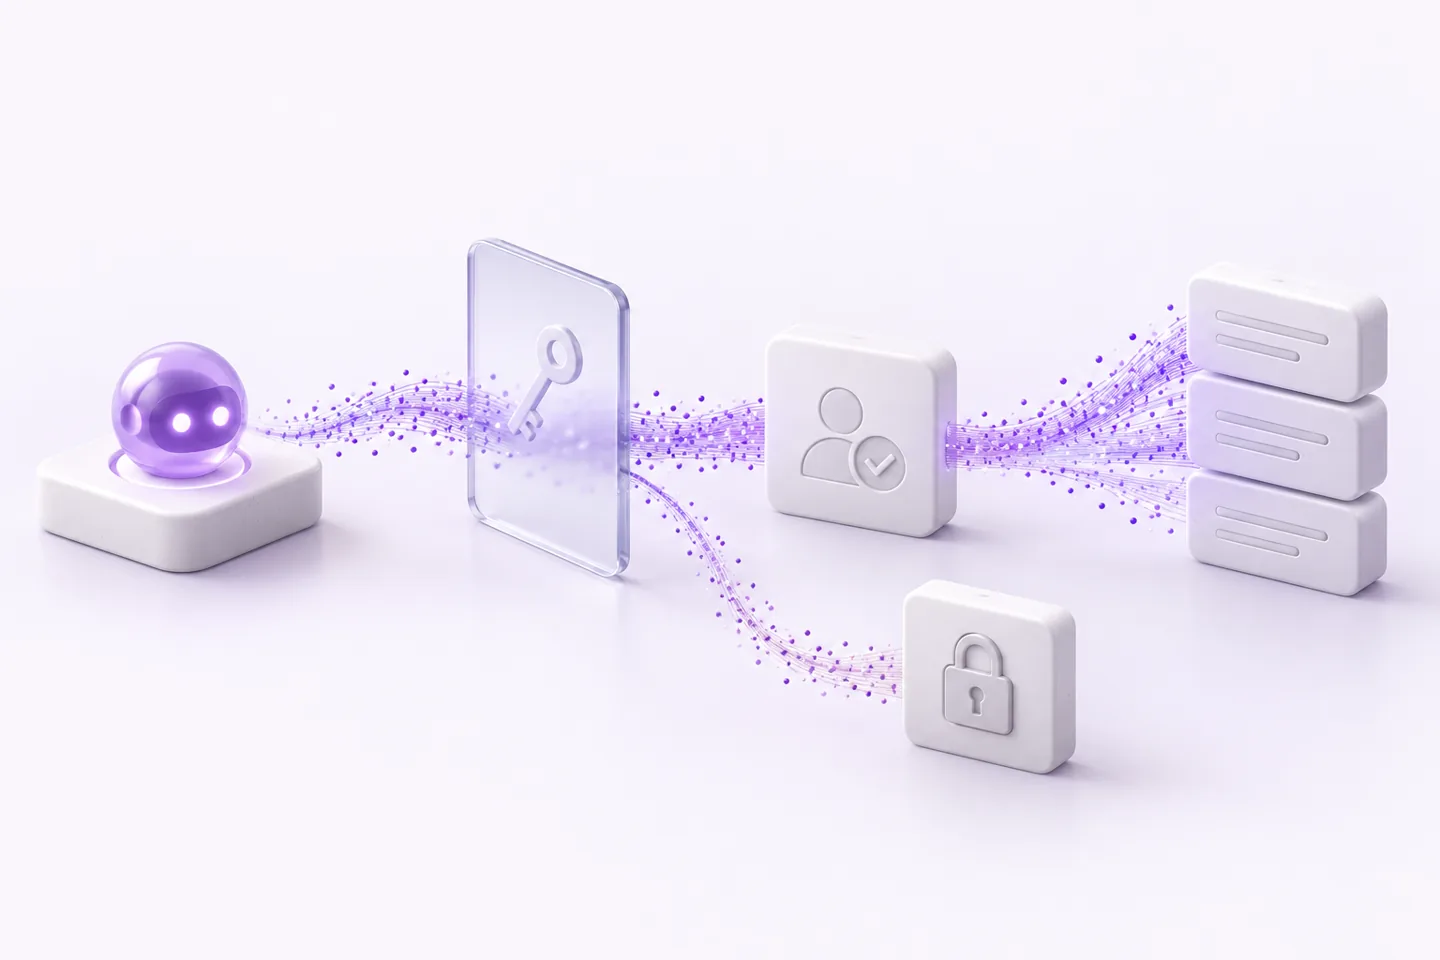
Combined according to the risk of each action.
Validate inputs and proposed actions against agreed rules before anything is written.
Require a person above a value, risk level or confidence limit.
Pause and hand over when information is missing or answers conflict.
Proportionate to the impact of each action.
Every action the agent may take.
What could go wrong and how reversible it is.
Checks, approvals and stop conditions per action.
Try edge cases before launch.
Actions can move from approval to automatic only with evidence and your agreement.
No. Changes to instructions, tools or thresholds are made by people, tested and approved before release.
The action is held and the case goes to the agreed person or queue with the reason.
We choose the model and provider for each task during scoping, based on the language, accuracy, latency and data-handling requirements. The workflow is not tied to one provider, so a step can be changed later if the agreed requirements change.
Discovery call
Bring us a process, a recurring enquiry or a pile of documents. We will explore where agents fit and what a useful implementation needs.
Book a discovery call