People
Roles for users, reviewers and administrators of the workflow.
Security & governance
Decide who can use, configure and approve each agent, and which systems the agent itself may reach.
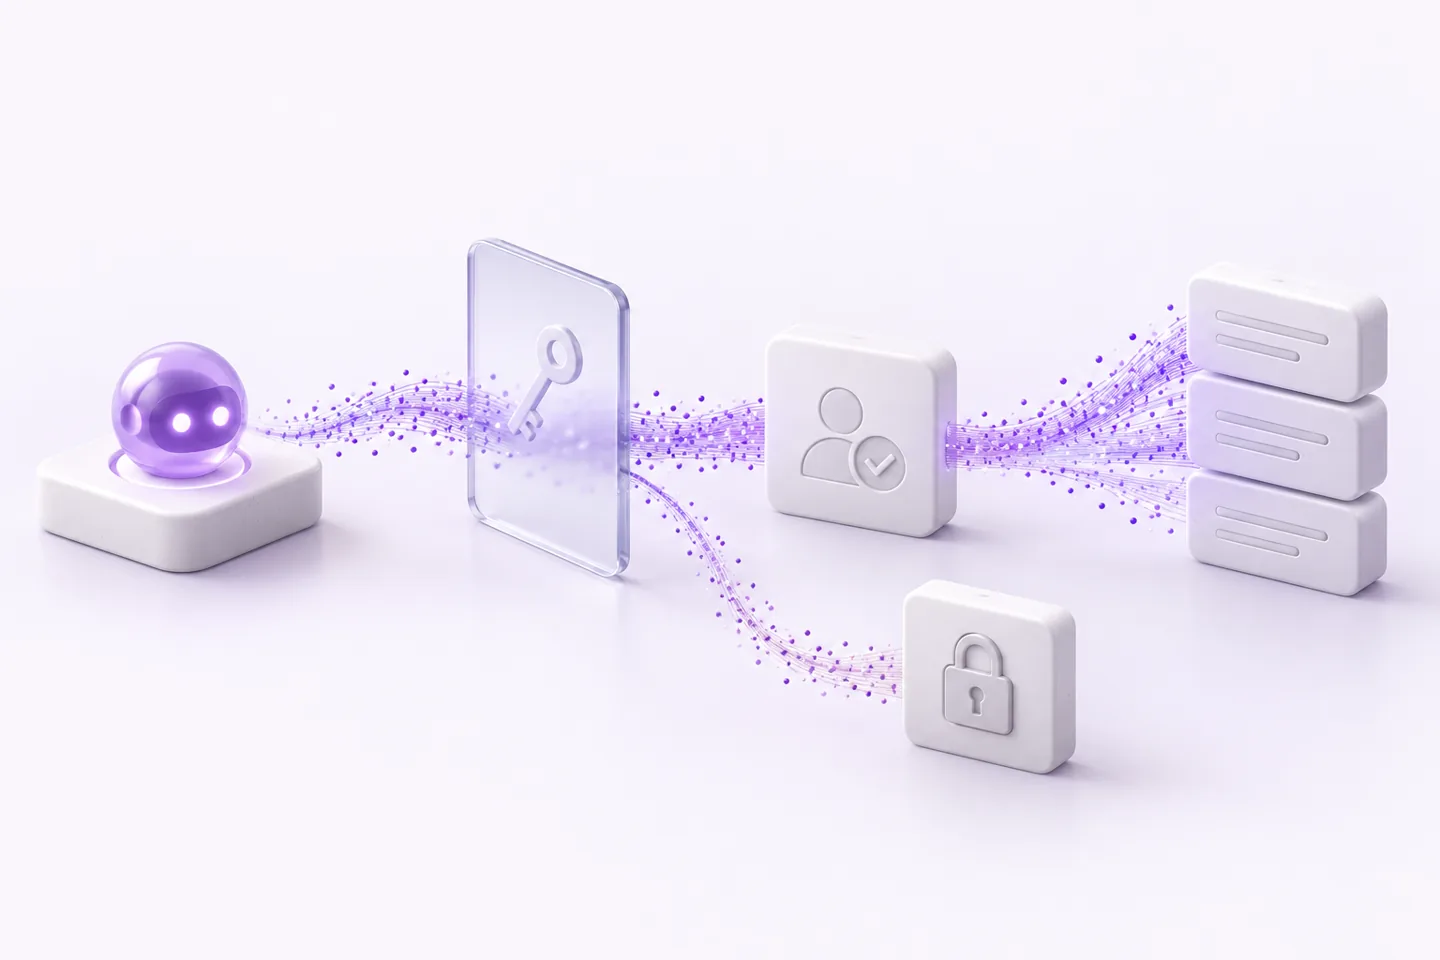
People and agents both get only the access they need.
Roles for users, reviewers and administrators of the workflow.
Service accounts and scopes for each connected system.
Data separated between customers and, where agreed, between teams.
Agreed per implementation.
Who can view, review, approve or change the workflow.
Which records and actions each connection allows.
Check access when people or workflows change.
Revoke access when it is no longer needed.
Broader access is a deliberate, recorded decision.
Where the components used in your implementation support it, we can discuss SSO during scoping.
Access for our team is limited to what is needed to build and support the workflow, and agreed with you.
We choose the model and provider for each task during scoping, based on the language, accuracy, latency and data-handling requirements. The workflow is not tied to one provider, so a step can be changed later if the agreed requirements change.
Discovery call
Bring us a process, a recurring enquiry or a pile of documents. We will explore where agents fit and what a useful implementation needs.
Book a discovery call